Krypto-Hacker nutzen das Aave-Tool eines Drittanbieters, um 114 ETH zu stehlen
Story summary
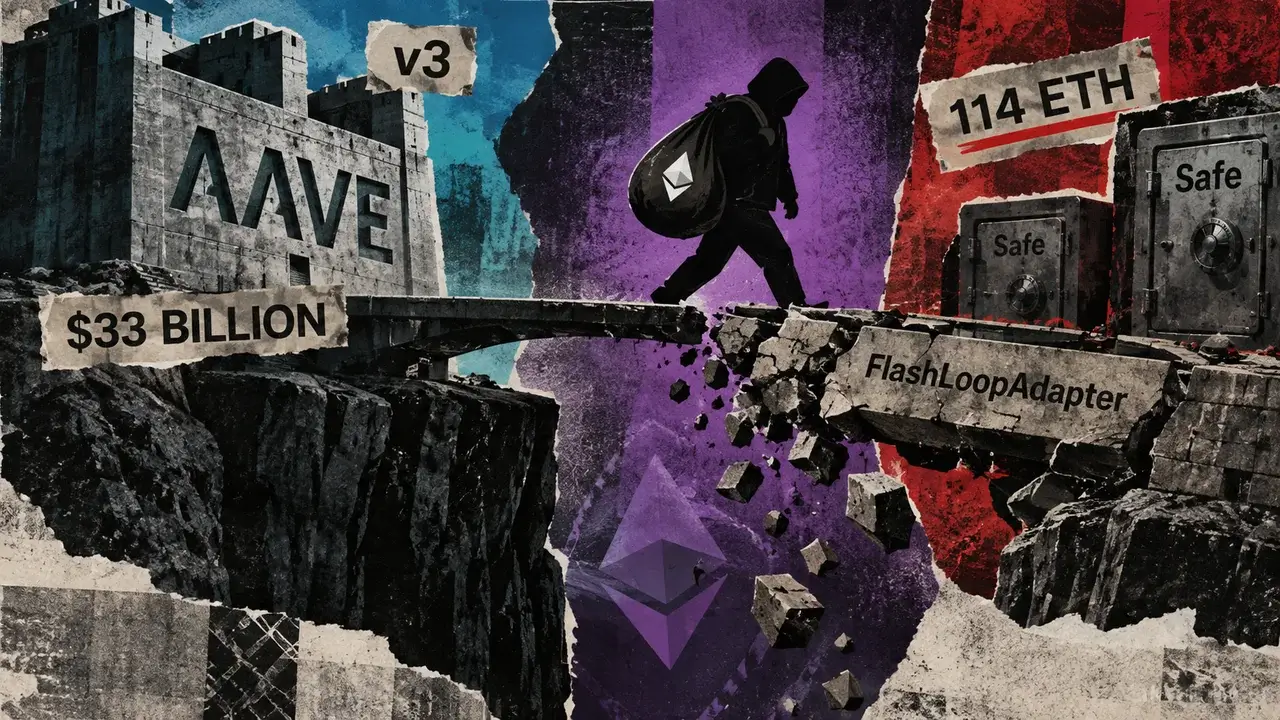
Ein auf Aave basierender Kreditadapter eines Drittanbieters wurde ausgenutzt, um etwa 114 ETH im Wert von über 300.000 US-Dollar zu stehlen, während das Protokoll selbst davon unberührt blieb. Am 2. Oktober sagte das Blockchain-Sicherheitsunternehmen SlowMist, der Angreifer habe zwei Safe-Multisig-Wallets durch einen Fehler im verwendeten FlashLoopAdapter kompromittiert
📌 Key Highlights & Takeaways
- Ein auf Aave basierender Kreditadapter eines Drittanbieters wurde ausgenutzt, um etwa 114 ETH im Wert von über 300.000 US-Dollar zu stehlen, während das Protokoll selbst davon unberührt blieb.
- Oktober sagte das Blockchain-Sicherheitsunternehmen SlowMist, der Angreifer habe zwei Safe-Multisig-Wallets durch einen Fehler im verwendeten FlashLoopAdapter kompromittiert
A third-party lending adapter built on Aave was exploited to steal about 114 ETH, worth over $300,000, while the protocol itself remained unaffected.
On Oct. 2, blockchain security firm SlowMist said the attacker compromised two Safe multisig wallets through a flaw in the FlashLoopAdapter used with Aave v3 positions. The exploit allowed the attacker to bypass the adapter’s authentication checks, execute arbitrary calls, and drain collateral from the affected wallets.
SlowMist estimated the direct loss at about 114.09 ETH. It said roughly 1,300 WETH of debt was also repaid during the attack to unlock collateral tied to the positions.
Aave founder Stani Kulechov said the incident did not involve Aave v3’s core smart contracts. He said :
“This is not Aave v3 contract, it’s third party external adapter built on top of Aave, zero effect on Aave v3.”
The distinction is significant for Aave, the largest decentralized lending protocol, with more than $33 billion in total value locked. The exploit affected infrastructure layered on top of Aave.
SlowMist traced the vulnerability to the FlashLoopAdapter’s open() and close() functions, which checked whether the calling Safe had enabled the adapter as a module.
According to SlowMist, the attacker created a fake Safe contract that always returned a positive response when asked whether the module was enabled. The adapter then accepted the forged authentication and proceeded to its internal swap function.
Crypto Profit & Yield Calculator
Simulate trading returns, staking APY, and crypto gains with real-time fee modeling.
Source: CryptoSlate.
Read the full story at the original source ↗
For questions: mrsmithcons@gmail.com.
💎 On-Chain Wallet Tracking & Breakout Targets
Direct wallet address monitoring, smart money flows, and liquidity depth.
⚡ Track Whale Wallets Now ➔More from CryptoAce VIP
 🚀 RocketCoin Casino
Beste Krypto-Casinos Malaysia 2026 – Top-Bitcoin-Casino-Tipps
Aktuelle Berichterstattung von escapistmagazine.com: Beste Krypto-Casinos Malaysia 2026 – Top-Bitcoin-Casino-T...
 ₿ Lucky Satoshi
SEC schlägt neue Regeln zur Kryptoverwahrung vor
Bitcoin Magazine SEC schlägt neue Regeln zur Krypto-Verwahrung vor Die Regulierungsbehörde schlug neue Regeln ...
 ⚡ LiveCoin Bet
Maxxed baut eine Mitgliedergemeinschaft auf, bevor sein Krypto-Casino und seine Sportwetten im Oktober 2026 live gehen
Aktuelle Berichterstattung von Yogonet: Maxxed baut eine Mitglieder-Community auf, bevor sein Krypto-Casino un...
 🎁 Get Rich Free
Die 5 besten Airdrop-Plattformen, denen Sie vor dem nächsten Bull Run (2026) folgen sollten
Aktuelle Berichterstattung von TechBullion: Die 5 besten Airdrop-Plattformen, denen man vor dem nächsten Bull ...