Rogue iPhone app escapes iOS sandbox to hijack $580,000 in USDT
Story summary
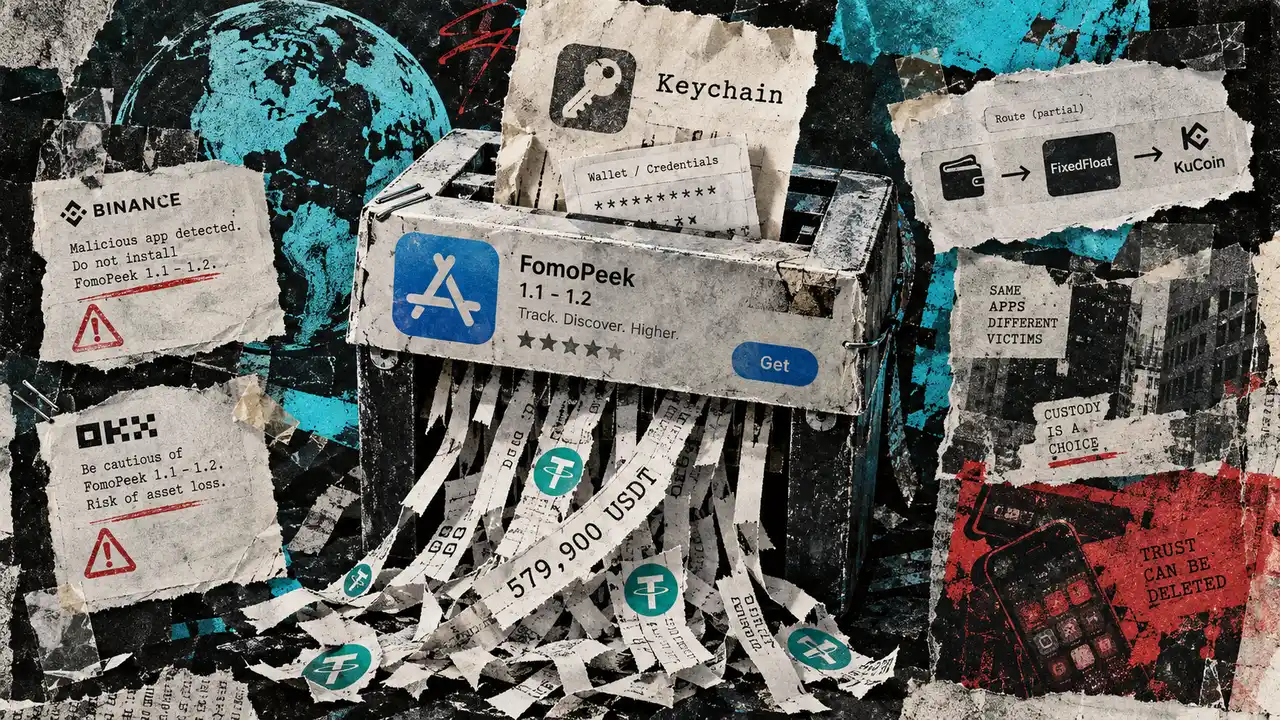
Fomopeek, a malicious iPhone app distributed through Apple’s App Store, has been linked to nearly $580,000 in stolen USDT. Blockchain security firm SlowMist began investigating the app over the weekend after receiving reports of stolen assets linked to exposed private keys. Some victims had previous
📌 Key Highlights & Takeaways
- Fomopeek, a malicious iPhone app distributed through Apple’s App Store, has been linked to nearly $580,000 in stolen USDT.
- Blockchain security firm SlowMist began investigating the app over the weekend after receiving reports of stolen assets linked to exposed private keys.
- Some victims had previous
Fomopeek, a malicious iPhone app distributed through Apple’s App Store, has been linked to nearly $580,000 in stolen USDT.
Blockchain security firm SlowMist began investigating the app over the weekend after receiving reports of stolen assets linked to exposed private keys.
Some victims had previously installed versions 1.1 or 1.2 of the Fomopeek app, which was marketed as a read-only tool for tracking large cryptocurrency transactions across Ethereum, Solana and Tron.
Working with security researchers at crypto exchange OKX, SlowMist found two modules embedded in those versions that had no connection to FomoPeek’s advertised monitoring functions.
One communicated with external command-and-control infrastructure, while the other contained a kernel exploitation framework with eight attack methods that could adjust to the victim’s iPhone model and operating-system version.
A successful exploit could escape Apple’s application sandbox and reach Keychain information and files belonging to other apps. That created a route to locally stored private keys, seed phrases, and login credentials without requiring users to connect a wallet or enter those details into FomoPeek.
SlowMist founder Yu Xian said the risk extended to passwords stored in Apple’s Keychain and encrypted files held by other applications. An attacker who obtained both could potentially unlock wallet credentials and other sensitive information stored on the device.
“After a successful attack, the app can break through the iOS sandbox isolation mechanism, then read and decrypt the system keychain (Keychain), and access data files from other apps on the device. Private keys, mnemonic phrases, login credentials, chat histories, files, and other user data stored on the device may all face the risk of leakage as a result. Additionally, the app connects to covert servers unrelated to its public business functions to receive remote instructions.”
Crypto Profit & Yield Calculator
Simulate trading returns, staking APY, and crypto gains with real-time fee modeling.
Source: CryptoSlate.
On-Chain Whale Radar: Smart Money Cold Wallet Outflows & High-Yield DeFi Opportunities
Uncover high-yield crypto alpha, on-chain whale accumulation alerts, 100x altcoin gems, and automated DeFi yield opportunities before the retail crowd.
Track Whale Wallets ➔💎 On-Chain Wallet Tracking & Breakout Targets
Direct wallet address monitoring, smart money flows, and liquidity depth.
⚡ Track Whale Wallets Now ➔More from CryptoAce VIP
 🚀 RocketCoin Casino
Why I Started Tracking My Crypto Gambling Wins (And You Should Too)
Breaking coverage reported by Coin Gabbar: Why I Started Tracking My Crypto Gambling Wins (And You Should Too)...
 🤖 FreeRich AI Hub
Apple will let EU apps use less-alarming tracking-consent screens
Apple is changing its App Tracking Transparency prompts in parts of Europe after competition regulators said t...
 ₿ Lucky Satoshi
Bitcoin’s Bull Run Is Back — and the Data Agrees
Bitcoin Magazine Bitcoin’s Bull Run Is Back — and the Data Agrees The Bitcoin price's move above its 365-day a...
 ⚡ LiveCoin Bet
5 bold predictions for the Bills offense in 2026
Making 5 bold predictions for the Bills offense during the 2026 NFL season.......