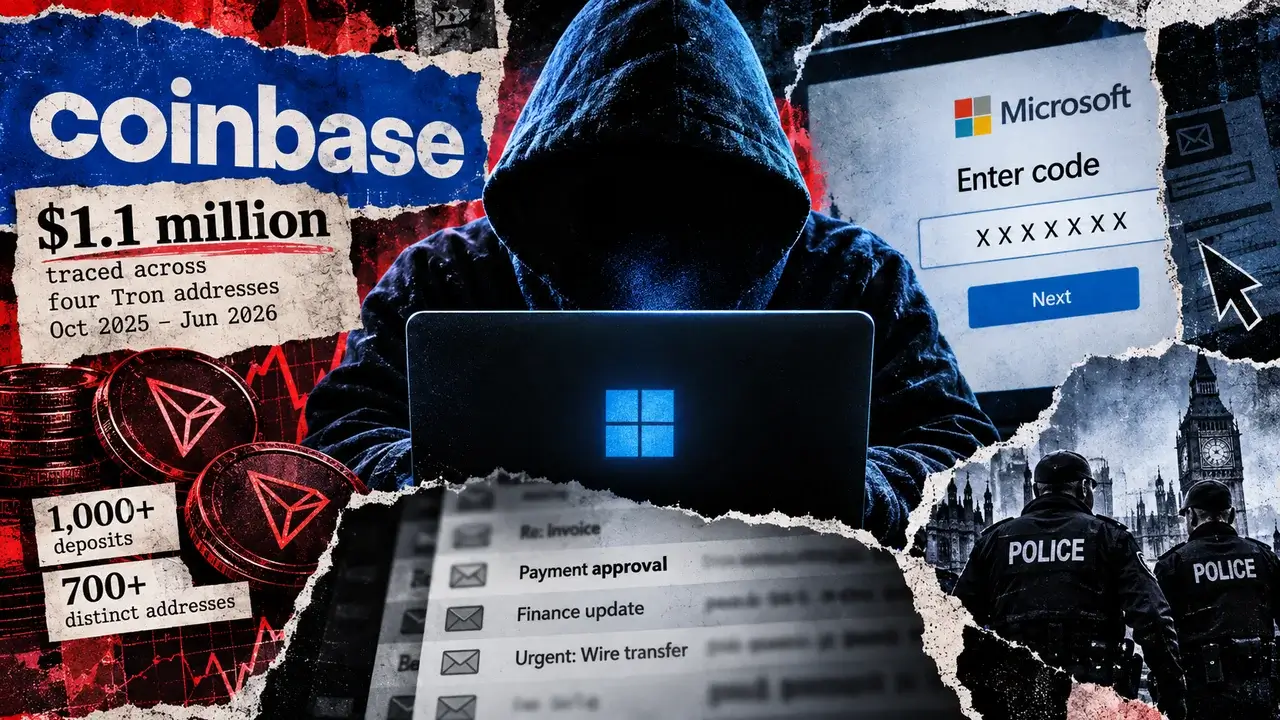
Coinbase traced $1.1 million crypto trail behind AI phishing service EvilTokens
Story summary
EvilTokens abused Microsoft’s real device-login flow to authorize attacker sessions, then used AI to identify payment authorities inside captured mailboxes. The post Coinbase traced $1.1 million crypto trail behind AI phishing service EvilTokens appeared first on CryptoSlate.
📌 Key Highlights & Takeaways
- EvilTokens abused Microsoft’s real device-login flow to authorize attacker sessions, then used AI to identify payment authorities inside captured mailboxes.
- The post Coinbase traced $1.1 million crypto trail behind AI phishing service EvilTokens appeared first on CryptoSlate.
Microsoft and Coinbase helped dismantle EvilTokens, an AI phishing service tied to more than 12,000 compromised inboxes worldwide.
The operation had reached more than 10,000 organizations within months of launching, spanning financial services, real estate, healthcare, construction and other industries, Microsoft said .
The company and its partners seized 50 websites used by EvilTokens and disabled more than 150 related domains, while UK police arrested two men on Sept. 11 on suspicion of offenses connected to the alleged operation. Police later released both on conditional bail.
EvilTokens had packaged much of the business-email-compromise process into a subscription service sold through Telegram . Microsoft said customers paid a $1,500 initiation fee and $500 recurring subscription for tools that combined account compromise, mailbox access, reconnaissance, and AI-assisted fraud preparation in a single interface.
The service’s entry point relied on Microsoft’s device-code authentication, a legitimate sign-in flow designed for hardware such as smart TVs and conferencing equipment that cannot easily support standard browser logins.
Attackers initiated the authentication request themselves, then sent the resulting code to targets through phishing emails disguised as invoices, shared files, and other routine business communications.
Victims who entered that code on Microsoft’s legitimate website effectively approved the session waiting on the attacker’s device.
The process could still require a password and multifactor authentication when the user was signed out, but those credentials remained on Microsoft’s infrastructure. The process generated authorization for the attacker-initiated session.
Crypto Profit & Yield Calculator
Simulate trading returns, staking APY, and crypto gains with real-time fee modeling.
Source: CryptoSlate.
On-Chain Whale Radar: Smart Money Cold Wallet Outflows & High-Yield DeFi Opportunities
Uncover high-yield crypto alpha, on-chain whale accumulation alerts, 100x altcoin gems, and automated DeFi yield opportunities before the retail crowd.
Track Whale Wallets ➔💎 On-Chain Wallet Tracking & Breakout Targets
Direct wallet address monitoring, smart money flows, and liquidity depth.
⚡ Track Whale Wallets Now ➔More from CryptoAce VIP
 🚀 RocketCoin Casino
Por que comecei a rastrear minhas vitórias em jogos criptográficos (e você também deveria)
Cobertura de última hora relatada por Coin Gabbar: Por que comecei a rastrear minhas vitórias em jogos de azar...
 ⚡ LiveCoin Bet
Betpanda Review: The Crypto Sportsbook Betting Without Limits, a $30,000 Weekly Tournament, and a 6,000-Game Casino Behind It
Breaking coverage: Betpanda Review: The Crypto Sportsbook Betting Without Limits, a $30,000 Weekly Tournament,...
The Dirty Secret Behind a Tiny Country's Wealth: Where the Elite Hide Their Billions
Think you know Luxembourg? Think again! Dive into the secrets behind Europe's richest country—where tiny size ...
 🎁 Get Rich Free
Airdrop tax: what applies in Germany
Breaking coverage reported by cryptoticker.io: Airdrop tax: what applies in Germany. Our news desk tracks ongo...