Os nós Eclair Bitcoin Lightning não corrigidos podem travar novamente sempre que forem reiniciados
Story summary
Novas divulgações mostram como os canais não financiados salvos podem sobrecarregar os nós mais antigos novamente na reinicialização, apesar de uma correção enviada em julho. A postagem Os nós Eclair Bitcoin Lightning sem patch podem travar novamente sempre que forem reiniciados apareceu pela primeira vez no CryptoSlate.
📌 Key Highlights & Takeaways
- Novas divulgações mostram como os canais não financiados salvos podem sobrecarregar os nós mais antigos novamente na reinicialização, apesar de uma correção enviada em julho.
- A postagem Os nós Eclair Bitcoin Lightning sem patch podem travar novamente sempre que forem reiniciados apareceu pela primeira vez no CryptoSlate.
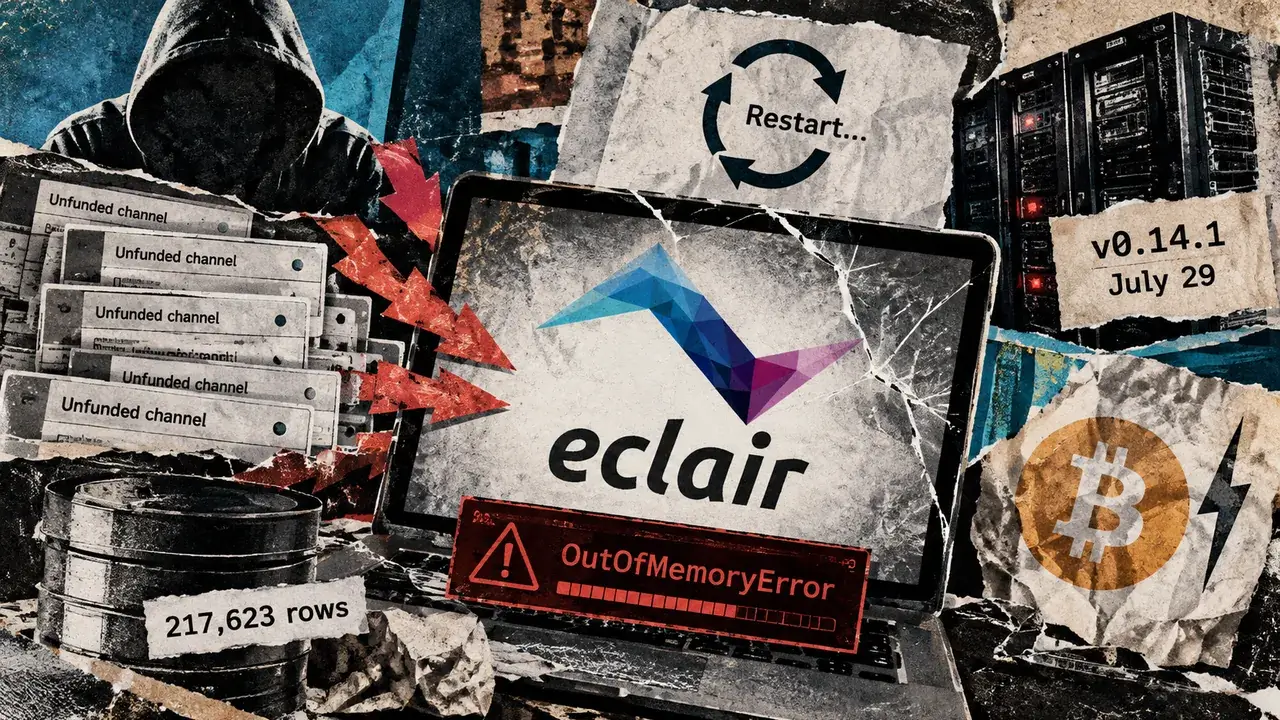
A newly disclosed unfunded-channel flaw could leave Eclair, a Bitcoin Lightning implementation, crashing repeatedly without an attacker spending BTC on-chain. The flaw affected reachable nodes running v0.14.0 and earlier, with saved channel records making a restart insufficient to restore service.
Researcher Erick Cestari published the persistent-crash finding Sept. 30 and explained it alongside a separate denial-of-service bug in an Oct. 1 developer post . Both were fixed in v0.14.1, released in July, before the public disclosures. ACINQ now recommends the later v0.14.3 security release for separate vulnerabilities.
Eclair limited the number of pending channels a peer could open, but inconsistent checks of temporary and final channel identifiers let its counter undercount unfunded channels. A malicious peer could accumulate saved requests without broadcasting the funding transaction or paying an on-chain fee.
That distinction matters: the BTC normally needed to fund a channel did not have to be committed for the vulnerable node to incur memory and database costs. The attack still required computing resources and network traffic.
In Cestari’s proof of concept, Eclair v0.14.0 ran in regtest, Bitcoin’s local testing environment. He reported that the node exhausted a 4 GB Java virtual machine heap after about 47 minutes 43 seconds, with 217,623 rows accumulated in the channel database. That is one laboratory benchmark, not a universal attack duration.
The initial crash left those records on disk. During startup, Eclair reloaded the channels and exhausted memory again. Cestari described increasing the heap or manually removing fake channel records as recovery measures. Repeated restarts left the underlying load in place.
The demonstration concerns one vulnerable node’s availability. It does not establish live exploitation or the number of unpatched nodes.
ACINQ merged PR #3324 July 17. The patch strengthened duplicate-channel checks, and v0.14.1 shipped July 29 . According to Erick Cestari / Delving Bitcoin, v0.14.0 and earlier are affected, while v0.14.1 or later addresses these two denial-of-service findings.
Crypto Profit & Yield Calculator
Simulate trading returns, staking APY, and crypto gains with real-time fee modeling.
Source: CryptoSlate.
Read the full story at the original source ↗
For questions: mrsmithcons@gmail.com.
💎 On-Chain Wallet Tracking & Breakout Targets
Direct wallet address monitoring, smart money flows, and liquidity depth.
⚡ Track Whale Wallets Now ➔More from CryptoAce VIP


 ₿ Lucky Satoshi
Frank Holmes: Eles imprimirão US$ 100 trilhões – Por que comprar Bitcoin e ouro
Revista Bitcoin Frank Holmes: Eles imprimirão US$ 100 trilhões – Por que comprar Bitcoin e ouro Os mineradores...
 🚀 RocketCoin Casino
Crypto Casinos 2026 - Bitcoin, Ethereum & Altcoin Casino Guide
Breaking coverage reported by 25yearslatersite.com: Crypto Casinos 2026 - Bitcoin, Ethereum & Altcoin Casino G...
 ⚡ LiveCoin Bet
O cofundador da Zcash apóia o Bitcoin protegido e afirma que sua meta de final de ano da ZEC ainda está em jogo
O cofundador da Zcash, Eli Ben-Sasson, apóia o Shielded Bitcoin para transferências privadas L1 e mantém uma m...
 🪙 FreeFortune Crypto
Atualizações ao vivo: Bitcoin gerencia pequenos ganhos à medida que as ações caem devido à preocupação com a IA e aumentos do petróleo [Revisado pelo analista sênior.]
A reunião de política monetária de dois dias do Federal Reserve começa amanhã, com quase todos esperando que o...