Альпен говорит, что AI обнаружил эксплойт BTC Liquid на сумму 320 миллионов долларов за час. Мог ли лимит выплат остановить это?
Story summary
Воспроизведение после атаки объясняет недостаток кэша, а SideSwap утверждает, что ордер на 4000 L-BTC не имел никаких ограничений по размеру или скорости. В сообщении Альпена говорится, что AI обнаружил эксплойт BTC Liquid на сумму 320 миллионов долларов за час. Мог ли лимит выплат остановить это? впервые появился на CryptoSlate.
📌 Key Highlights & Takeaways
- Воспроизведение после атаки объясняет недостаток кэша, а SideSwap утверждает, что ордер на 4000 L-BTC не имел никаких ограничений по размеру или скорости.
- В сообщении Альпена говорится, что AI обнаружил эксплойт BTC Liquid на сумму 320 миллионов долларов за час.
- Мог ли лимит выплат остановить это?
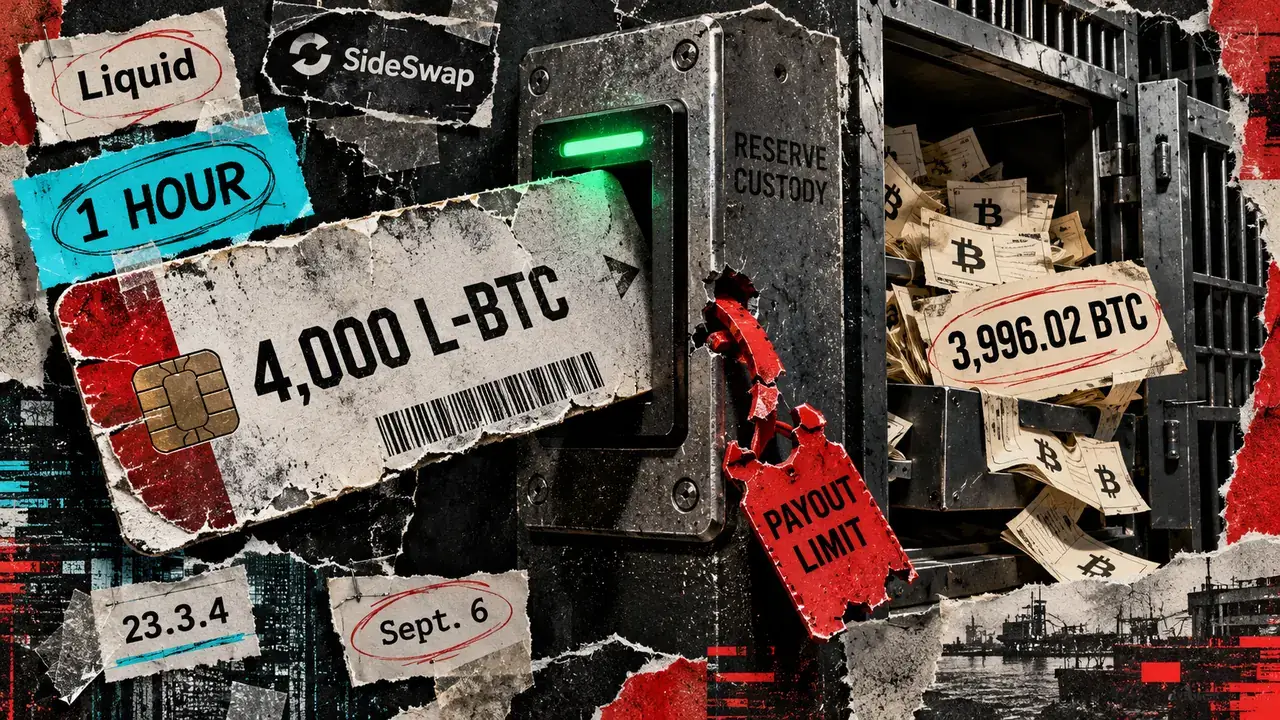
On September 6, 2026, Liquid’s federation released roughly 3,996 BTC after its network accepted L-BTC that lacked Bitcoin backing. Liquid is a Bitcoin sidechain whose L-BTC is meant to represent bitcoin held in a federation reserve. A validly authorized withdrawal turned the invalid sidechain state into a real Bitcoin payment worth about $320 million at the time. A payout limit before federation signing might have interrupted that exit.
Alpen Labs CEO Simanta Gautam now says his AI agents traced the flaw and reproduced it locally in about an hour. The work began after he heard of the September 6 attack. His September 22 account and technical report give a detailed explanation of the failed proof check. The demonstration came after the funds left, so its speed says little by itself about whether a standing AI monitor would have raised an actionable warning before the attack.
Elements, the software underlying Liquid, caches successful checks of the cryptographic proofs attached to confidential transactions. A September 1 code change tried to make each cached result depend on all the context that affects verification, including the asset generator and output script. Alpen says the change concatenated those fields as raw bytes without encoding their boundaries. A valid “seed” proof and a different, invalid target could therefore produce identical cache input.
In Alpen’s local replay, fresh verification rejected the target, while the affected cache wrapper accepted it after the seed had populated the cache. A successful cache lookup bypassed the proof check that should have rejected the target. The two statements had the same input bytes for the cache even though they represented different verification requests. This was a local reproduction of the suspected consensus failure. Alpen says exact production validator binaries and historical cache contents were unavailable, leaving the deployed code and live priming path strongly inferred from the source and chain evidence.
SideSwap says a private security build installed on its own node in August accepted the attack transaction. That account narrows the deployment question for one operator but does not identify every federation functionary’s build. On September 8, an Elements repair changed cache keys to encode field lengths, added collision-focused tests and introduced an option to bypass the range-proof cache. Version 23.3.4 followed on September 9. Those changes address the validation gate before invalid L-BTC can become accepted state.
According to SideSwap’s account , the attacker sent 4,000 L-BTC to its peg-out service at 14:05 UTC on September 6. SideSwap burned the tokens with valid authorization at 14:06. The order exceeded its own wallet funds, causing two attempted payouts to fail before federation signers released 3,996 BTC at 14:28. SideSwap says it forwarded 3,995.99999857 BTC to the customer’s address in the same Bitcoin block.
The accepted order shows why a valid key was insufficient as a safety check. SideSwap says its authorization key was online, payouts were automatic, and its service had no size, velocity, supply-relative, wallet-history or human-review checks. The federation also signed an exceptional request after the two failed attempts. A payout limit or other independent hold at the service or federation, applied before authorization or signing, could have stopped this particular payout path even after Liquid admitted invalid state.
An offline authorization key would have created a pause before SideSwap approved the peg-out. A delayed manual forward would have acted later. It could have left the Bitcoin paid by the federation under SideSwap’s control for return, but the federation’s reserve transfer would already have occurred. The precise place a safeguard acts determines which loss it can prevent.
Crypto Profit & Yield Calculator
Simulate trading returns, staking APY, and crypto gains with real-time fee modeling.
Source: CryptoSlate.
Read the full story at the original source ↗
For questions: mrsmithcons@gmail.com.
On-Chain Whale Radar: Smart Money Cold Wallet Outflows & High-Yield DeFi Opportunities
Uncover high-yield crypto alpha, on-chain whale accumulation alerts, 100x altcoin gems, and automated DeFi yield opportunities before the retail crowd.
Track Whale Wallets ➔💎 On-Chain Wallet Tracking & Breakout Targets
Direct wallet address monitoring, smart money flows, and liquidity depth.
⚡ Track Whale Wallets Now ➔More from CryptoAce VIP

 🚀 RocketCoin Casino
В списке лучших крипто-казино — 5 лучших сайтов для азартных игр на биткойны с мгновенными выплатами (2026 г.)
Новое освещение, опубликованное Muddy River Sports: список лучших криптоказино – 5 лучших сайтов для азартных ...
 ₿ Lucky Satoshi
Брент Джонсон: BTC — лучший актив «чистой игры» для повышения глобальной ликвидности
Журнал «Биткойн» Брент Джонсон: BTC — лучший актив «чистой игры» для повышения глобальной ликвидности Биткойн-...
 ⚡ LiveCoin Bet
A Better Trade Than Bitcoin or Gold in 2026 Is Sitting in Your Kitchen
Raw sugar futures have gained roughly 20% in 2026, outpacing Bitcoin (BTC), gold, and the S&P 500 as the Europ...
 🪙 FreeFortune Crypto
Jito Surges 39% As Solana Liquid Staking Competition Heats Up
Breaking coverage: Jito Surges 39% As Solana Liquid Staking Competition Heats Up. Comprehensive monitoring, on...