Крипто-хакеры используют сторонний инструмент Aave, чтобы украсть 114 ETH
Story summary
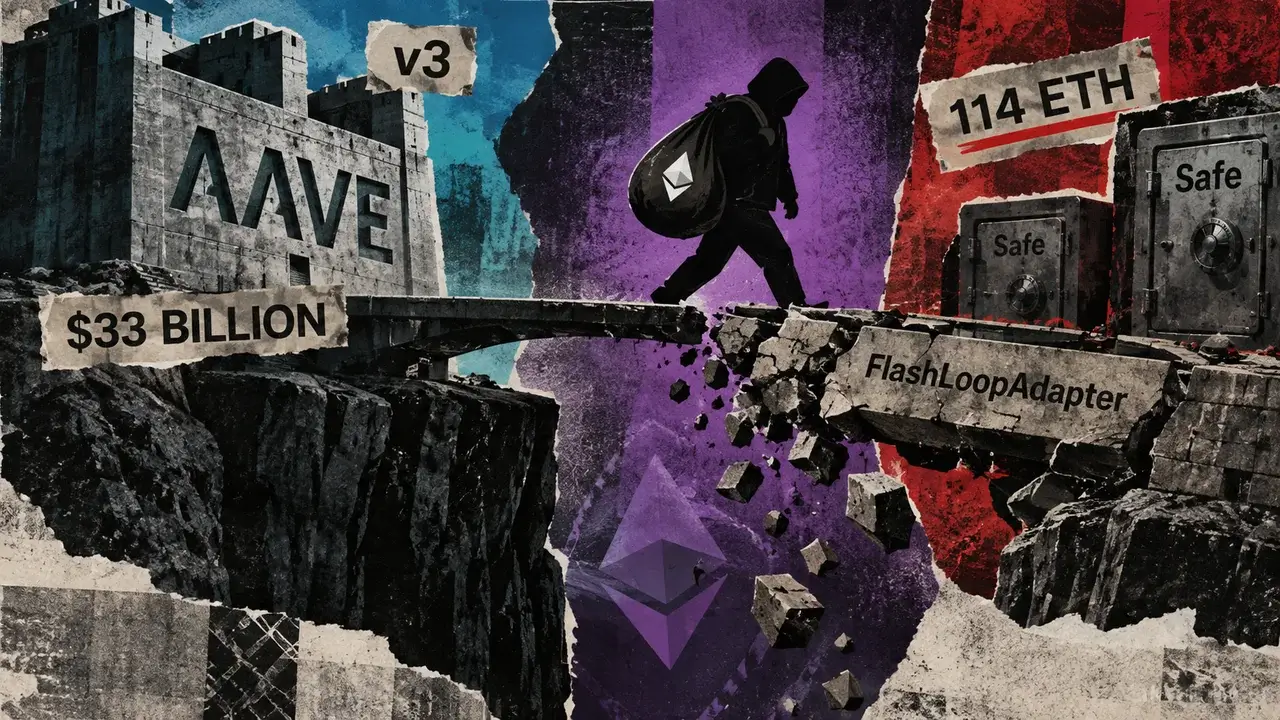
Сторонний адаптер кредитования, построенный на Aave, был использован для кражи около 114 ETH на сумму более 300 000 долларов США, при этом сам протокол остался незатронутым. 2 октября компания SlowMist, занимающаяся безопасностью блокчейнов, заявила, что злоумышленник скомпрометировал два мультиподписных кошелька Safe из-за уязвимости в FlashLoopAdapter, используемом с
📌 Key Highlights & Takeaways
- Сторонний адаптер кредитования, построенный на Aave, был использован для кражи около 114 ETH на сумму более 300 000 долларов США, при этом сам протокол остался незатронутым.
- 2 октября компания SlowMist, занимающаяся безопасностью блокчейнов, заявила, что злоумышленник скомпрометировал два мультиподписных кошелька Safe из-за уязвимости в FlashLoopAdapter, используемом с
A third-party lending adapter built on Aave was exploited to steal about 114 ETH, worth over $300,000, while the protocol itself remained unaffected.
On Oct. 2, blockchain security firm SlowMist said the attacker compromised two Safe multisig wallets through a flaw in the FlashLoopAdapter used with Aave v3 positions. The exploit allowed the attacker to bypass the adapter’s authentication checks, execute arbitrary calls, and drain collateral from the affected wallets.
SlowMist estimated the direct loss at about 114.09 ETH. It said roughly 1,300 WETH of debt was also repaid during the attack to unlock collateral tied to the positions.
Aave founder Stani Kulechov said the incident did not involve Aave v3’s core smart contracts. He said :
“This is not Aave v3 contract, it’s third party external adapter built on top of Aave, zero effect on Aave v3.”
The distinction is significant for Aave, the largest decentralized lending protocol, with more than $33 billion in total value locked. The exploit affected infrastructure layered on top of Aave.
SlowMist traced the vulnerability to the FlashLoopAdapter’s open() and close() functions, which checked whether the calling Safe had enabled the adapter as a module.
According to SlowMist, the attacker created a fake Safe contract that always returned a positive response when asked whether the module was enabled. The adapter then accepted the forged authentication and proceeded to its internal swap function.
Crypto Profit & Yield Calculator
Simulate trading returns, staking APY, and crypto gains with real-time fee modeling.
Source: CryptoSlate.
Read the full story at the original source ↗
For questions: mrsmithcons@gmail.com.
💎 On-Chain Wallet Tracking & Breakout Targets
Direct wallet address monitoring, smart money flows, and liquidity depth.
⚡ Track Whale Wallets Now ➔More from CryptoAce VIP
 🚀 RocketCoin Casino
Лучшие крипто-казино Малайзии 2026 – лучшие биткойн-казино
Новое освещение, опубликованное escapistmagazine.com: Лучшие крипто-казино Малайзии 2026 года — лучшие биткойн...
 ₿ Lucky Satoshi
SEC предлагает новые правила хранения криптовалют
Журнал Bitcoin Magazine SEC предлагает новые правила хранения криптовалют Регулятор предложил новые правила, к...
 ⚡ LiveCoin Bet
Maxxed создает сообщество участников до запуска своего крипто-казино и букмекерской конторы в октябре 2026 года.
Срочное освещение, о котором сообщает Yogonet: Maxxed создает сообщество участников до того, как его крипто-ка...
 🎁 Get Rich Free
5 лучших платформ Airdrop, которым стоит следовать перед следующим бычьим забегом (2026 г.)
Новое освещение, опубликованное TechBullion: 5 лучших платформ Airdrop, которым следует следовать перед следую...