Neues Bitcoin-Upgrade fängt versteckte Schlüssellecks auf, die die genaue Lösung verbergen
Story summary
BIP461 würde konforme ECDSA-Signaturen reproduzierbar machen und Vergleiche ermöglichen, die Abweichungen kennzeichnen, ohne schädliche Firmware nachzuweisen. Der Beitrag Neues Bitcoin-Upgrade fängt versteckte Schlüssellecks auf, die den genauen Fix verbergen, erschien zuerst auf CryptoSlate.
📌 Key Highlights & Takeaways
- BIP461 würde konforme ECDSA-Signaturen reproduzierbar machen und Vergleiche ermöglichen, die Abweichungen kennzeichnen, ohne schädliche Firmware nachzuweisen.
- Der Beitrag Neues Bitcoin-Upgrade fängt versteckte Schlüssellecks auf, die den genauen Fix verbergen, erschien zuerst auf CryptoSlate.
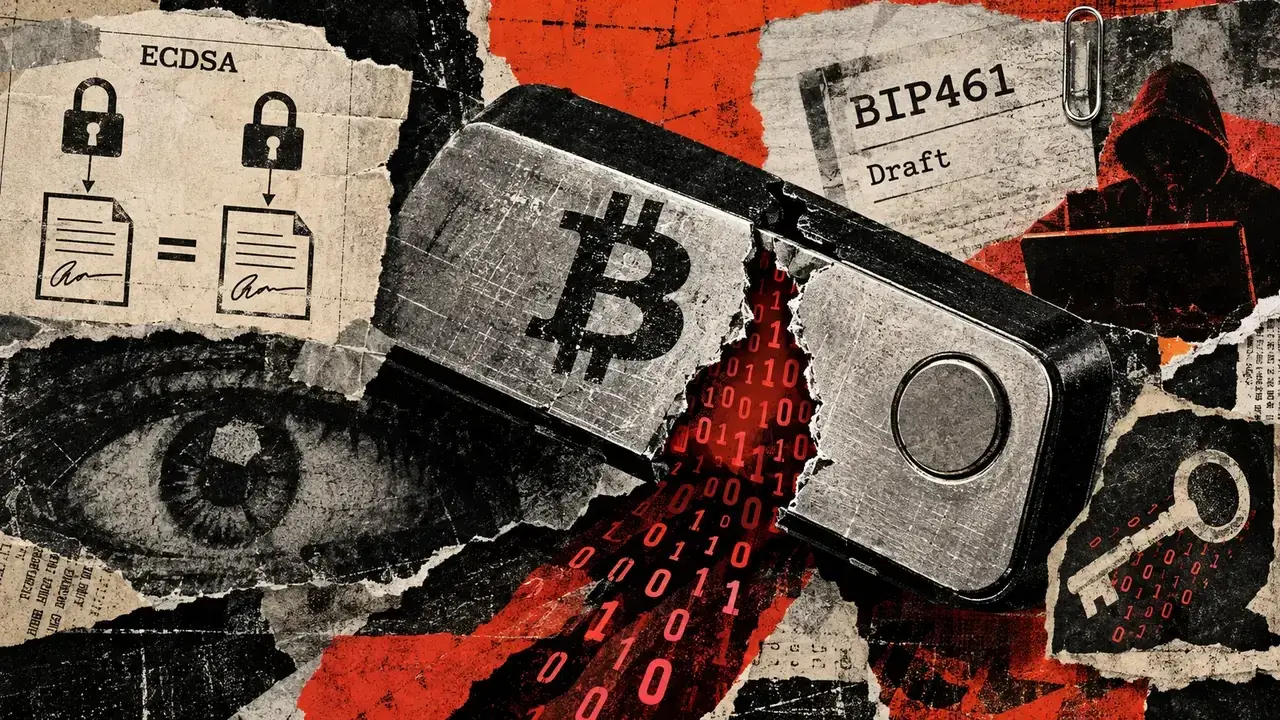
Bitcoin improvement proposal BIP461 could make a hidden route for leaking wallet secrets easier to detect. The draft defines a common signing procedure for ECDSA, an existing Bitcoin signature scheme.
Independent compliant signers should produce identical signatures for the same secret key and message hash, creating a benchmark for detecting departures that could conceal key leakage.
Authored by Liam Gilligan, the proposal was merged into the BIPs repository on Sept. 16 and remains marked Draft. Its signatures work under existing Bitcoin consensus rules, so implementing this signing procedure requires no consensus change.
ECDSA allows a signer choices while creating a valid signature, including the nonce, a temporary value used in signing. Malicious firmware can exploit that freedom to hide key material in signatures that still pass verification, and BIP461 fixes those choices through a specified deterministic procedure.
Bitcoin’s acceptance of a signature cannot establish that its creation kept the key safe. A common specification supplies an expected output against which the signer’s behavior can be checked.
The comparison requires identical inputs and the exact same standard, including access to the secret key on another independent signer. That extra exposure is a practical cost of reproducing the signature. Different results for the same key and message hash show that at least one signer is not following BIP461.
An honest implementation using another valid ECDSA procedure can also disagree. A mismatch warrants investigation into compliance, but its cause remains unresolved. The comparison alone cannot identify a malicious device or demonstrate theft.
The prescribed algorithm also keeps signatures to at most 70 bytes in the standard DER encoding, excluding Bitcoin’s one-byte sighash flag.
Crypto Profit & Yield Calculator
Simulate trading returns, staking APY, and crypto gains with real-time fee modeling.
Source: CryptoSlate.
Read the full story at the original source ↗
For questions: mrsmithcons@gmail.com.
💎 On-Chain Wallet Tracking & Breakout Targets
Direct wallet address monitoring, smart money flows, and liquidity depth.
⚡ Track Whale Wallets Now ➔More from CryptoAce VIP
 🚀 RocketCoin Casino
Best Crypto Casinos 2026 – 5 Fastest Bitcoin Gambling Sites Ranked by Trust
Breaking coverage: Best Crypto Casinos 2026 – 5 Fastest Bitcoin Gambling Sites Ranked by Trust. Comprehensive ...
 ₿ Lucky Satoshi
Bitcoin-Datenschutzdurchbruch ein Zcash-Killer? | Misha Komorov, Alloc Innit
Bitcoin Magazine Bitcoin-Datenschutzdurchbruch ein Zcash-Killer? | Misha Komorov, Alloc Innit Misha Komarov er...
 ⚡ LiveCoin Bet
Der Mitbegründer von Zcash unterstützt Shielded Bitcoin und sagt, dass sein ZEC-Jahresziel noch immer im Spiel sei
Zcash-Mitbegründer Eli Ben-Sasson unterstützt Shielded Bitcoin für private L1-Transfers und bleibt bei einem Z...
 🪙 FreeFortune Crypto
Live-Updates: Bitcoin erzielt kleine Gewinne, da die Aktien aufgrund von KI-Bedenken und steigenden Ölpreisen fallen [Überprüft von Senior Analyst.]
Morgen beginnt die zweitägige geldpolitische Sitzung der Federal Reserve, und fast alle gehen nun davon aus, d...